HACK THE BOX / SHERLOCK · DFIR
NoSignal: following the CCTV traffic
Analyzing CCTV network traffic to uncover port scanning, credential attacks, unauthorized camera access, and video stream disruptions using TShark.
NOTES FROM THE LAB
Investigations and project writeups. The clues I followed, the decisions I made, and what I learned.
FOLLOW THE CONNECTIONS
Explore the topics in the field notes below.
HACK THE BOX / SHERLOCK · DFIR
Analyzing CCTV network traffic to uncover port scanning, credential attacks, unauthorized camera access, and video stream disruptions using TShark.
HACK THE BOX / SHERLOCK · THREAT HUNTING
Tracing a disguised executable, C2 connections, and attacker commands through Sysmon logs to reconstruct the attack and firewall response.
HACK THE BOX / SHERLOCK · DFIR
Analyzing Chrome and AnyDesk artifacts to trace a tech support scam and reconstruct the attacker’s remote access.
HACK THE BOX / MACHINE
Exploiting an unauthenticated FreePBX SQL injection for RCE and an incron-triggered file sourcing vulnerability for root privilege escalation.
NETWORK ANALYSIS
A collection of Wireshark investigations focused on packet analysis, protocol behavior, network reconnaissance, authentication traffic, and encrypted communications.
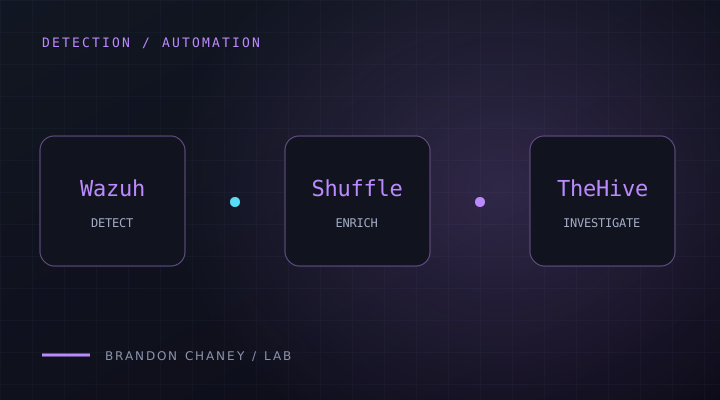
DETECTION & AUTOMATION
Built an end-to-end detection, enrichment, and incident response workflow using Sysmon, Wazuh, Shuffle, VirusTotal, and TheHive.
Full writeups open on GitHub.
The learning behind the investigations.
Explore my certifications